Singapore Digital Infrastructure Act: 3MW and 10MW Scope
Singapore’s Digital Infrastructure Act 2026 establishes licensing regimes for major cloud and data centre services, but detailed operating rules are still being developed. For infrastructure buyers, cloud resilience testing and contract checks now need to account for the Act’s scope while separating
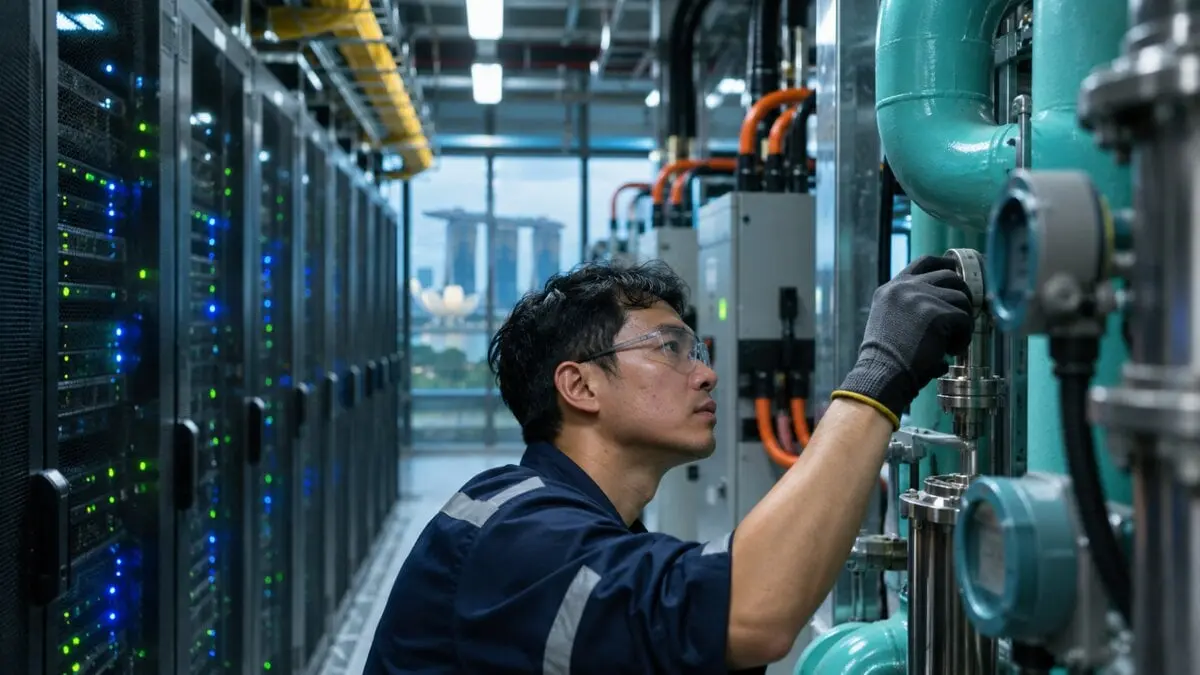
Singapore’s Digital Infrastructure Act 2026 establishes licensing regimes for major cloud and data centre services, but detailed operating rules are still being developed. For infrastructure buyers, cloud resilience testing and contract checks now need to account for the Act’s scope while separating its enacted framework from obligations expected to commence in 2027.
- Act No. 25 of 2026 establishes separate security and resilience licensing and data centre sustainability licensing.
- Its stated thresholds are 10 MW for major data centre facility services, S$100 million in qualifying cloud revenue, and 3 MW for data centre sustainability licensing.
- Final technical requirements require implementing instruments; purchasing compliance software does not establish compliance.
- The Act was passed on 7 October 2026, assented to on 29 October and first published in the Government Gazette on 10 November. The minister said commencement is expected in 2027; detailed Codes of Practice and regulations are still being developed.
Which Providers Fall Within the Published Licensing Framework?
MDDI’s September announcement describes a major-provider regime covering co-location and cloud data centres with a critical IT load of at least 10 MW. For cloud services, it identifies Infrastructure-as-a-Service and Platform-as-a-Service generating at least S$100 million in average annual revenue from Singapore users over the preceding three years.
The Act also establishes a separate sustainability licence for data centres with critical IT load of at least 3 MW. These are different tests: falling below the major-provider threshold does not establish that a facility falls outside sustainability licensing.
The minister’s opening speech explains that critical IT load means the maximum electrical power designed for IT equipment, rather than electricity consumed at a particular moment. It also distinguishes finished Software-as-a-Service applications from the IaaS and PaaS categories targeted by the major-cloud regime.
For procurement, ask suppliers to identify the contracting entity, operating entity, facility and service category separately. A corporate group’s size alone is insufficient evidence that the particular service meets the published test.
An enterprise buying cloud capacity should not assume that purchasing the service makes it a licensed infrastructure provider. Equally, an enterprise operating its own substantial data centre should examine the separate sustainability scope. The opening speech expressly includes internal-use facilities meeting that regime’s threshold. These distinctions concern operational responsibility, rather than the customer’s nationality.
Security and Sustainability Require Different Evidence
MDDI’s announcement describes security risk management, business continuity, disaster recovery and reporting specified incidents or disruptions to IMDA. Its framework addresses operational failures as well as cybersecurity. Buyers should therefore request evidence covering cooling, power and recovery dependencies alongside critical infrastructure cybersecurity services.
The minister’s October second-reading speech says detailed technical rules will sit in regulations and Codes of Practice. It describes facility-level energy efficiency, measured through Power Usage Effectiveness, as the initial sustainability focus, with equipment and water-efficiency requirements potentially introduced later.
The official consultation response hosted by REACH also identifies unresolved implementation questions, including cloud revenue attribution and critical IT load assessment. It explains the intention to recognise existing audits where possible and differentiate requirements according to operational control.
Translate those distinctions into supplier questions. Request the boundary of each audit, the date of the latest recovery exercise, unresolved findings and the person responsible for remediation. Ask whether energy efficiency monitoring systems measure the facility being purchased, rather than an unrelated portfolio average.
Data centre compliance software should preserve source measurements, approvals and corrective actions. Before buying, require a demonstration using your reporting workflow and evidence-retention needs; avoid accepting a generic compliance dashboard as proof of readiness.
The related commercial constraints are covered in JournalArta’s guide to Singapore data centre capacity and resource constraints. For this procurement exercise, keep capacity availability separate from evidence that the selected facility can meet its applicable requirements.
Compare Scope Before Comparing Compliance Costs
The table compares procurement situations using the ministry’s published framework. Buyer profiles and recommended checks are editorial analysis. No standard compliance-package price was disclosed in the official framework materials reviewed; “not disclosed” does not mean free.
| Procurement situation | Published technical scope | Principal duty or check | Compliance price, USD | Main procurement benefit and ideal user |
|---|---|---|---|---|
| Major co-location facility | Critical IT load of at least 10 MW | Examine security, recovery and sustainability scope | Not disclosed | Facility-level evidence for enterprise hosting buyers |
| Major cloud data centre | Critical IT load of at least 10 MW | Separate facility responsibilities from cloud-service responsibilities | Not disclosed | Responsibility mapping for cloud infrastructure teams |
| Qualifying IaaS or PaaS service | At least S$100 million average annual Singapore-user revenue over three preceding years | Confirm service classification and revenue attribution | Not disclosed | Scope assessment for platform procurement teams |
| Internal-use enterprise data centre | Critical IT load of at least 3 MW under the sustainability framework | Examine facility energy-efficiency requirements | Not disclosed | Upgrade planning for enterprise facility operators |
Testing tools provide a narrower, separately priced purchase. AWS Fault Injection Service lists $0.10 per action-minute outside AWS GovCloud, with another $0.10 per action-minute for each additional target account. Optional experiment reports cost $5 each.
Those are tool charges, not a Singapore compliance budget. Request separate estimates for test design, infrastructure consumption, engineering time, remediation and assurance. A low experiment charge cannot establish the cost of restoring a business service.
When estimating migration or recovery costs, use JournalArta’s AWS, Azure and Google Cloud egress-fee comparison alongside supplier quotations. Keep transfer charges separate from testing, monitoring and regulatory preparation.
What Buyers Should Require Before Signing
For an operator planning facility upgrades, commission a scope assessment before specifying monitoring software. Require a metering plan, ownership of measurement data and a staged remediation budget. Ask bidders to distinguish existing capabilities from work dependent on final technical rules.
For a cloud buyer, prioritise evidence that the application can recover. Request a recovery demonstration, dependency map and incident communication process. Choose testing services according to the systems and failure scenarios they can exercise, with clear approval and stopping procedures.
For a co-location customer, document who controls facility power and cooling, customer equipment and application recovery. Put evidence access, incident cooperation and responsibility for corrective work into the contract. Require any proposed compliance surcharge to identify its scope, deliverables and pricing basis.
Timing remains a qualification. In his closing speech, Tan Kiat How said commencement was expected in 2027, with existing operators given six months from commencement to apply and permission to continue while applications were considered. That statement is a policy expectation, not verification of an appointed commencement date or a universal upgrade deadline.
The purchasing decision should rest on documented scope, observable recovery performance and a costed implementation plan. A supplier’s regulatory-readiness claim becomes useful when the buyer can inspect the underlying evidence and assign responsibility for gaps.
- MDDI framework announcement, published 8 September 2026; accessed 16 November 2026.
- MDDI opening speech, dated 6 October 2026; accessed 16 November 2026.
- MDDI closing speech, dated 7 October 2026; accessed 16 November 2026.
- REACH consultation and government response, accessed 16 November 2026.
- AWS Fault Injection Service pricing, accessed 16 November 2026; publication date not stated.
 Take the quizWhat Kind of Holiday Spender Are You? Take the Black Friday QuizStart →
- 1I’m A Celebrity 2026 Line-Up: Rooney Leads 11 Stars Into Jungle

- 2Mavericks Surfers Race to California for Waves Near 50 Feet
- 3NYC Medical Examiner Has Not Determined Cause of Death of Beau Rose Jessup
- 4Mountaineer Finds Ice Age Cave Bear Graveyard in the Dolomites
- 5Rugby League World Cup Final 2026: Kick-Off Times and How to Watch Kangaroos v New Zealand
 Lifestyle7 Signs Your Social Battery Is Running Low (and Why You Keep Cancelling Plans)
 Lifestyle · Food & HealthThanksgiving Food Safety: How Long Leftovers Last and the Safe Turkey Temperature
 Lifestyle7 Quiet Habits of Emotionally Intelligent People, According to Psychologists
 LifestylePeople Who Don’t Like Celebrating Their Birthday Often Share These 7 Traits