UK Cloud Security Posture Management: AWS vs Azure vs GCP
A technical and cost comparison of AWS Security Hub, Microsoft Defender for Cloud, Google Cloud Security Command Center, and Wiz for UK regulated workloads under NCSC and FCA rules.
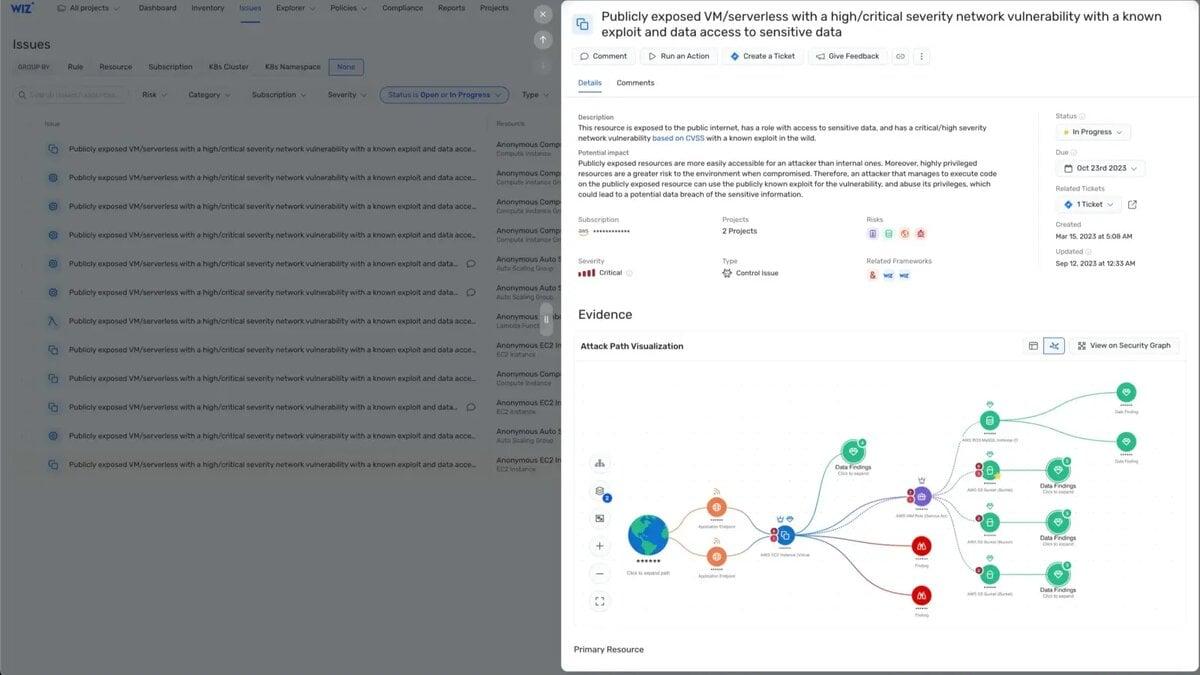
For UK-regulated enterprises, native cloud security posture management tools such as AWS Security Hub and Microsoft Defender for Cloud offer lower entry costs than third-party CNAPP platforms, yet multi-cloud governance under the NCSC and FCA rules quickly shifts the total cost equation. Choosing between AWS Security Hub, Microsoft Defender for Cloud, Google Cloud Security Command Center, and Wiz depends on the billing mechanics, the agentless scanning depth, and the audit evidence mapping.
- AWS Security Hub CSPM: Charges $0.0010 per security check for the first 100,000 monthly checks per account and Region, dropping to $0.0005 above 500,000 checks, with separate AWS Config item fees.
- Microsoft Defender for Cloud: Foundational CSPM is $0, while paid Defender CSPM bills roughly $5.00 to $5.11 per billable resource per month across VMs, databases, and storage accounts.
- Google Cloud Security Command Center: Standard tier is $0, Premium tier is priced at 5% of projected annual Google Cloud spend under $15 million or via pay-as-you-go, and Enterprise tier shuts down on May 21, 2027.
- UK Regulatory Alignment: Mapping controls to the NCSC 14 Cloud Security Principles and FCA operational resilience expectations requires continuous audit logs, external interface checks, and supply chain visibility.
UK Regulatory Requirements Under NCSC and FCA
UK financial institutions and critical infrastructure operators must demonstrate continuous control over their cloud configurations rather than relying on point-in-time reviews. The National Cyber Security Centre (NCSC) sets out 14 Cloud Security Principles that cover data in transit protection, asset protection and resilience, separation between customers, external interface protection, and audit information and alerting for customers.
In parallel, the Financial Conduct Authority (FCA) operational resilience framework requires firms to identify important business services, set impact tolerances, and maintain a mapping of underlying technology and third-party cloud dependencies. When technical teams pair the network controls that are covered in our ZTNA Zero Trust for UK Firms analysis with automated posture checks, they generate machine-readable evidence for internal risk committees and external auditors.
Free tiers rarely satisfy FCA auditability requirements on their own. While baseline posture scores surface obvious misconfigurations such as public storage buckets, regulated UK teams need attack-path analysis, IAM privilege graphing, and historical drift tracking to verify that operational resilience tolerances remain intact after routine infrastructure deployments.
Enterprise Pricing and Billing Mechanics Compared
Cloud security posture management pricing diverges sharply between per-check, per-resource, and spend-percentage models, which makes workload architecture the primary driver of monthly GBP (£) and USD ($) expenditure. Before committing to an annual contract, procurement teams should model their exact resource counts alongside the regional hosting baselines that are outlined in our AWS London vs Azure UK South vs Google Cloud Costs guide.
| Platform | Published Pricing Model (USD) | Multi-Cloud & Scanning Depth | Ideal UK Enterprise Profile |
|---|---|---|---|
| AWS Security Hub CSPM | $0.0010/check (first 100k); $0.0008 (100k–500k); $0.0005 (>500k); first 10k ingested findings free, then $0.00003/event | Deep AWS native checks; requires AWS Config; third-party findings ingestion is supported | AWS-centric UK firms with predictable account counts and automated remediation pipelines |
| Microsoft Defender for Cloud | Foundational CSPM: $0; Defender CSPM: ~$5.00–$5.11/billable resource/month (VMs, databases, storage; 2 containers or 8 functions = 1 unit) | Multi-cloud (Azure, AWS, GCP); agentless vulnerability scanning, attack path analysis, cloud security graph | UK enterprises that run Azure UK South alongside hybrid or multi-cloud workloads |
| Google Cloud Security Command Center | Standard: $0; Premium: 5% of projected annual GCP spend (<$15M) or PAYG; Enterprise tier is deprecated (shutdown May 21, 2027) | Native GCP asset inventory, threat detection, attack path simulation; Enterprise multi-cloud migrating to Premium | GCP-heavy engineering teams that seek unified threat detection tied to cloud spend |
| Wiz CSPM (CNAPP) | Annual per-workload subscription (public list pricing is not disclosed by the vendor) | Agentless multi-cloud graph across AWS, Azure, GCP, Kubernetes, and code-to-cloud pipelines | Large multi-cloud UK financial firms that need one unified graph for audit and SecOps teams |
On AWS, teams must factor in AWS Config recording fees alongside AWS Security Hub pricing because every enabled security standard evaluates configuration items continuously. Enabling multiple overlapping standards does not double-bill identical controls on the same resource, yet high-churn container environments can still drive up check volumes rapidly.
Provider-by-Provider Cost Drivers: Azure and Google Cloud
On Microsoft Azure, Microsoft Defender for Cloud pricing shields network policies, subnets, and IAM role assignments from per-unit billing by charging only on primary compute, database, and storage resources. For serverless teams, two running serverless containers or eight serverless functions count as a single billable resource, which keeps posture costs predictable during traffic spikes.
On Google Cloud, Google Cloud Security Command Center pricing ties Premium subscription fees to 5% of committed or projected annual GCP spend below $15 million. Because Google Cloud is retiring its Enterprise tier on May 21, 2027 and migrating active organizations to Premium, UK architects who are evaluating multi-cloud CNAPP coverage should verify whether Premium covers their non-GCP accounts without separate tooling.
Operational Trade-offs: Native Tools vs Independent CNAPP
Native CSPM suites eliminate procurement friction and keep telemetry inside the cloud provider's regional boundary, such as AWS Europe (London) or Azure UK South. Security operations engineers can trigger native event-driven remediations without exporting sensitive IAM graphs to an external SaaS control plane, which simplifies data residency reviews under UK GDPR and NCSC Principle 2 on asset protection.
Independent platforms such as Wiz address a different bottleneck: fragmented alert queues across three cloud consoles. When a UK bank operates production workloads in AWS London, analytics in Google Cloud, and identity in Microsoft Entra ID, correlating lateral movement across clouds becomes difficult with single-vendor tools. Independent CNAPP platforms unify vulnerability, identity, and network exposure into one queryable graph, though at an undisclosed enterprise subscription cost that sits on top of native cloud bills.
Another architectural factor is alert fatigue. Simply turning on CIS Benchmarks or NCSC-mapped policies across legacy accounts generates thousands of low-priority findings. Security teams must invest engineering hours into suppression rules, IaC (Infrastructure as Code) pre-deployment scanning, and automated ticketing regardless of whether they select a native suite or a third-party platform.
Decision Framework for UK IT and Security Leaders
Choose AWS Security Hub CSPM if more than 80% of your regulated workloads sit inside AWS London and your FinOps team can enforce strict AWS Config retention policies. Choose Microsoft Defender for Cloud (Defender CSPM) if your core estate runs on Azure UK South or hybrid Arc-connected servers and you want transparent per-resource pricing that includes AWS and GCP visibility without separate vendor contracts.
Select Google Cloud Security Command Center Premium if Google Cloud is your primary environment and a 5% spend-linked fee fits your FinOps budget, while accounting for the May 2027 Enterprise tier sunset. Opt for an independent multi-cloud CNAPP such as Wiz only when cross-cloud attack path correlation and unified FCA compliance reporting outweigh the added SaaS licensing cost.
 Take the quizWhat Kind of Holiday Spender Are You? Take the Black Friday QuizStart →
 Markets · FintechHow to Calculate Compound Interest: Formula, Examples and the Rule of 72
 Lifestyle · Food & HealthNormal Blood Pressure Chart by Age: Healthy Ranges Explained
 Lifestyle · Food & HealthWhat Is Raynaud’s Syndrome? Why Fingers Turn White in the Cold
 Lifestyle · Food & Health4 Ways Walking After Meals Helps Your Body, Doctors Say