White House AI Task Force Urges Leniency on Cyberattack Penalties
The Trump administration's AI task force urged federal regulators to hold off on enforcement against companies hit by AI-driven cyberattacks. It wants the leniency to run at least 12 months and to encourage voluntary reporting of vulnerabilities and incidents, according to its statement after Thursday's meeting.
The Trump administration's AI task force on Thursday urged federal regulatory agencies not to take enforcement actions against companies that suffer cyberattacks after AI overwhelms their defenses, in the latest cybersecurity news from Washington.
The group said the flexibility should last at least the next 12 months, "with the possibility of extension based on an ongoing evaluation of the risk landscape."
Why the task force wants a lighter touch
The task force said the threat picture has shifted. "It is clear that the cybersecurity risk environment has changed and organizations that only a short time ago had reasonable protections in place are now more vulnerable," it said in a statement about its second meeting.
As a result, it said, "prior standards for taking regulatory action against organizations in response to cyber incidents may be outdated."
Agencies should instead "implement limitations on regulatory liability for good-faith voluntary reporting of cybersecurity vulnerabilities and incidents," the task force said. That applies when it is "lawful, practical, and consistent with the interests of the American people, including public health and safety."
The goal is to ease rules that could "have a chilling effect on reporting and information sharing at a time when reporting is critical to our broad risk mitigation efforts," the group said.
Reporting rules and business complaints
Businesses have repeatedly told the federal government that overlapping and contradictory cybersecurity regulations are a burden. Some companies say compliance pulls resources away from incident response and defensive upgrades. The Trump administration, like its predecessor, has been looking for ways to cut regulatory complexity.
A forthcoming incident-reporting rule from the Cybersecurity and Infrastructure Security Agency (CISA) could add to that complexity. The task force said it supports the rulemaking and hopes CISA sets "clear and practical reporting requirements that minimize duplication."
What officials discussed
The meeting focused on the cybersecurity implications of advancing AI capabilities, according to a White House readout. Officials stressed coordination among federal, state and local governments and the private sector.
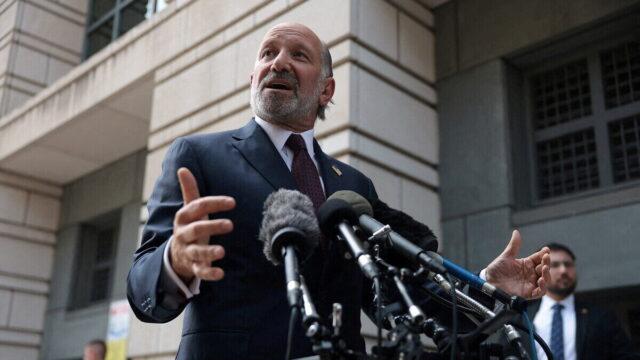
Commerce Secretary Howard Lutnick and National Cyber Director Sean Cairncross described work to identify and reduce security risks tied to new AI models. The National Security Agency and the National Institute of Standards and Technology have been testing new frontier models in partnership with major AI labs.
Cairncross and Emil Michael, the Pentagon's top research official, discussed talks with industry leaders about a process for voluntary reporting of AI-related incidents. Under that framework, the government would analyze reported incidents and share information with the private sector to help companies defend against similar threats.
Push to renew the 2015 sharing law
The task force also repeated the administration's support for a long-term reauthorization of the 2015 Cybersecurity Information Sharing Act. The law, which is close to expiring, gives companies liability protections when they share cyber threat data.
"Critical infrastructure operators and industry partners should be encouraged to proactively identify, report, and remediate cybersecurity risks without fear that good-faith voluntary disclosures will expose them to punitive regulatory or administrative action or civil liability," the group said.